無料のドメイン証明書を取得できるLet’s Encyptの利用手順のTipsです。
Let’s Encrypt
すべてのWebサーバへの接続を暗号化することを目指したプロジェクトである[4]。支払い、サーバ設定、メールによる確認、証明書の更新といった作業を省略することで、TLS暗号化における設定や保守の複雑さを大幅に削減することを意図している[5]。LinuxのWebサーバーでは、HTTPSの暗号化の設定および証明書の入手・更新がわずか2つのコマンドによって可能である
@see Let’s Encrypt
常時SSL化など、SSLのサイトが当たり前になってきました。サーバ証明書は安いもので1,000円、高いものだと数十万しますが、Let’s Encryptを利用すると無料でドメイン証明書を入手することが出来ます。
Certbotのインストール
# cd /usr/local/src
# git clone https://github.com/certbot/certbot
# cd certbot/
# ./certbot-auto -n

Complete!
Creating virtual environment...
Installing Python packages...
Installation succeeded.
Saving debug log to /var/log/letsencrypt/letsencrypt.log
Missing command line flags. For non-interactive execution,
you will need to specify a plugin on the command line.
Run with '--help plugins' to see a list of options,
and see https://eff.org/letsencrypt-plugins for more detail on what the plugins do and how to use them.
証明書の作成
# ./certbot-auto certonly --standalone -d example.com,www.example.com -m postmaster@example.com --agree-tos -n

Saving debug log to /var/log/letsencrypt/letsencrypt.log
Obtaining a new certificate
Performing the following challenges:
tls-sni-01 challenge for example.com
tls-sni-01 challenge for www.example.com
Cleaning up challenges
Problem binding to port 443: Could not bind to IPv4 or IPv6.
- -d ドメイン名
-d example.com, www.example.comなどwwwありなしに複数対応出来ます。 - -m 連絡用メールアドレス
問題発生
Problem binding to port 443: Could not bind to IPv4 or IPv6.
Nginx起動中は認証が未だに出来ない模様なのですよね…。
Nginxをとめます。
# systemctl stop nginx
証明書の認証
# ./certbot-auto certonly --standalone -d example.com,www.example.com -m postmaster@example.com --agree-tos -n


Saving debug log to /var/log/letsencrypt/letsencrypt.log
Obtaining a new certificate
Performing the following challenges:
tls-sni-01 challenge for sys-guard.com
tls-sni-01 challenge for www.sys-guard.com
Waiting for verification...
Cleaning up challenges

IMPORTANT NOTES:
 - Congratulations! Your certificate and chain have been saved at:
   /etc/letsencrypt/live/sys-guard.com/fullchain.pem
   Your key file has been saved at:
   /etc/letsencrypt/live/example.com/privkey.pem
   Your cert will expire on 2017-11-22. To obtain a new or tweaked
   version of this certificate in the future, simply run certbot-auto
   again. To non-interactively renew *all* of your certificates, run
   "certbot-auto renew"
 - If you like Certbot, please consider supporting our work by:

   Donating to ISRG / Let's Encrypt:   https://letsencrypt.org/donate
   Donating to EFF:                    https://eff.org/donate-le
起動させます。
# systemctl start nginx
証明書が作られています。
# ls -laht /etc/letsencrypt/live/example.com/

total 12K
drwxr-xr-x 2 root root 4.0K Aug 24 18:56 .
-rw-r--r-- 1 root root  543 Aug 24 18:56 README
drwx------ 3 root root 4.0K Aug 24 18:56 ..
lrwxrwxrwx 1 root root   37 Aug 24 18:56 cert.pem -> ../../archive/example.com/cert1.pem
lrwxrwxrwx 1 root root   38 Aug 24 18:56 chain.pem -> ../../archive/example.com/chain1.pem
lrwxrwxrwx 1 root root   42 Aug 24 18:56 fullchain.pem -> ../../archive/example.com/fullchain1.pem
lrwxrwxrwx 1 root root   40 Aug 24 18:56 privkey.pem -> ../../archive/example.com/privkey1.pem
Nginxの設定箇所にLets Encrypt証明書を追加しましょう。
        ssl_certificate_key /etc/letsencrypt/live/example.com/privkey.pem;
        ssl_certificate /etc/letsencrypt/live/example.com/fullchain.pem;
        ssl_protocols TLSv1 TLSv1.1 TLSv1.2;
# nginx -t
# systemctl reload nginx
これで反映されます。
反映されたかを見てみよう。
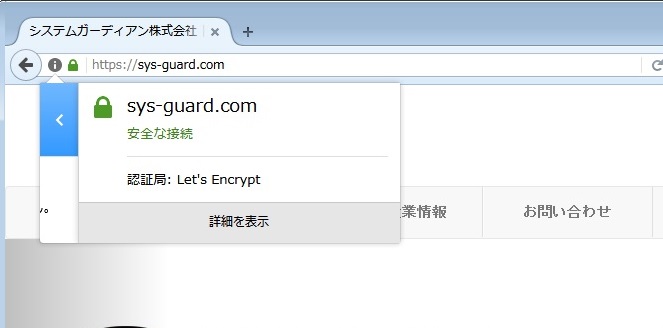
Let’s Encryptは90日以内に更新が必要です!
Cronを使って自動化します。
更新の自動化
# vi /etc/crontab

0 4 1 * * root /bin/systemctl stop nginx && /usr/local/src/certbot/certbot-auto renew --force-renewal && /bin/systemctl start nginx
# systemctl restart crond
問題があって、証明書の更新の毎に10~15秒WEBサービスを落とさないといけません。
Let’s Encryptが使えるケース
月に1回20秒ぐらい落ちても平気。
個人ブログや趣味のサイトなど許容できる場合はLet’s Encryptの恩恵を受けることは出来ます。
許容できないので、GeoTrustに戻します。
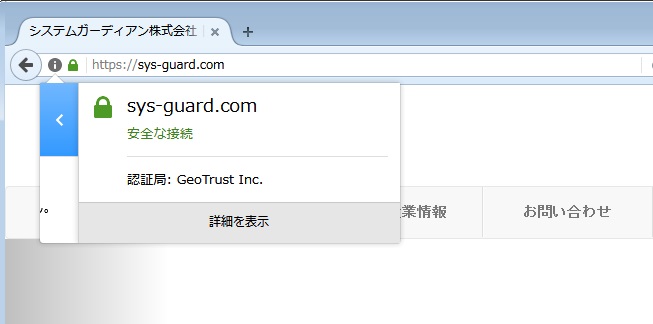
やはり更新毎に会社のサイトが10秒程落ちるのは許容できるか…。一番アウトなのはNginxが立ち上がりに失敗して長時間落ちっぱなしになってしまうケースが想定されるのはまずい。
今回はGeoTrustの証明書に戻しました。Nginxを止めずにLet’s Encryptが認証できるようになるまで保留かな?
お疲れ様です。