こんにちは、インフラ担当のちぇんです。
今回は以下の目的で DNS サーバを用意しようと思います。
・自宅の仮想環境が増えてきたので、 IP アドレスではなく名前解決できると楽かも
・サーバやネットワークの検証用
準備
概要
・サーバを 2 台、それぞれマスターとスレーブで構築しサーバ間の通信を暗号化します。
・ウェブサーバを IP アドレスではなくドメインでアクセスできるようにします。
今回のネットワーク構成
| 項目 | ホスト名 | IPv4 アドレス |
| ドメイン | local-dns-server | 192.168.1.0/24 |
| マスターサーバ | ns1.local-dns-server | 192.168.1.207 |
| スレーブサーバ | ns2.local-dns-server | 192.168.1.217 |
| WWWサーバ | yakiniku.local-dns-server | 192.168.1.52 |
bind インストール
# yum install bind bind-chroot bind-libs
ポート開放
# firewall-cmd --parmanent --add-service=dns
# firewall-cmd --reload
chroot でサービス起動
セキュリティを考慮し chroot で動かそうと思います。
# systemctl start named-chroot
# systemctl status named-chroot
# systemctl enable named-chroot
TSIG でサーバ間通信の暗号化
・ローカル環境ではありますが、暗号化通信の設定も行います。
共有鍵の作成
# dnssec-keygen -a hmac-md5 -b 128 -n HOST master-slave
Kmaster-slave.+157+17607
共有鍵の確認
# grep Key Kmaster-slave.+157+17607.private
Key: 6q5MpifXpE2X5VYPNngXQw==
設定ファイル編集
/etc/named.conf は、マスター・スレイブそれぞれで作成しますが、正引き・逆引きのファイルはマスターからスレイブへ提供するためマスター側でしか作成しません。
マスターサーバの設定
# /var/named/chroot/etc/named.conf

//
// named.conf
//
// Provided by Red Hat bind package to configure the ISC BIND named(8) DNS
// server as a caching only nameserver (as a localhost DNS resolver only).
//
// See /usr/share/doc/bind*/sample/ for example named configuration files.
//
// See the BIND Administrator's Reference Manual (ARM) for details about the
// configuration located in /usr/share/doc/bind-{version}/Bv9ARM.html

options {
listen-on port 53 { 192.168.1.207; };
// 127.0.0.1; };
// listen-on-v6 port 53 { ::1; };
directory "/var/named";
dump-file "/var/named/data/cache_dump.db";
statistics-file "/var/named/data/named_stats.txt";
memstatistics-file "/var/named/data/named_mem_stats.txt";
recursing-file "/var/named/data/named.recursing";
secroots-file "/var/named/data/named.secroots";
allow-query { any; };

/*
- If you are building an AUTHORITATIVE DNS server, do NOT enable recursion.
- If you are building a RECURSIVE (caching) DNS server, you need to enable
recursion.
- If your recursive DNS server has a public IP address, you MUST enable access
control to limit queries to your legitimate users. Failing to do so will
cause your server to become part of large scale DNS amplification
attacks. Implementing BCP38 within your network would greatly
reduce such attack surface
*/
recursion no;

dnssec-enable yes;
dnssec-validation yes;

/* Path to ISC DLV key */
bindkeys-file "/etc/named.root.key";

managed-keys-directory "/var/named/dynamic";

pid-file "/run/named/named.pid";
session-keyfile "/run/named/session.key";
};

logging {
channel default_debug {
file "data/named.run";
severity dynamic;
};
};

zone "." IN {
type hint;
file "named.ca";
};

include "/etc/named.rfc1912.zones";
include "/etc/named.root.key";

key "master-slave" {                    // 共有鍵の設定
algorithm hmac-md5;
secret "6q5MpifXpE2X5VYPNngXQw==";
};

zone "Local-DNS-Server" IN {
type master;
file "Local-DNS-Server.db";
allow-update { none; };
allow-transfer { 192.168.1.217; };
notify yes;
};

zone "1.168.192.in-addr.arpa" {
type master;
file "1.168.192.in-addr.arpa.db";
allow-update { none; };
allow-transfer { 192.168.1.217; };
notify yes;
};
IPv4 正引きマスターファイルの作成
# vi /var/named/Local-DNS-Server.db

$TTL 86400 ; 1D
@ IN SOA ns1.Local-DNS-Server. root.ns1.Local-DNS-Server. (
2020110501 ; serial
3600 ; refresh
600 ; retry
259200 ; expire
86400 ; minimum
)
IN NS ns1.Local-DNS-Server.
IN NS ns2.Local-DNS-Server.
yakiniku IN A 192.168.1.52
ns1 IN A 192.168.1.207
ns2 IN A 192.168.1.217
www IN CNAME yakiniku
IPv4 逆引きマスターファイルの作成
PTR レコードの左端の数字ですが・・・
最初は通し番号でいいんじゃね?と思って失敗しました。。。
IP アドレスとドメインの対応表なので、第 4 オクテットですよね(汗
# vi /var/named/1.168.192.in-addr.arpa.db

$TTL 86400
@ IN SOA ns1.Local-DNS-Server. root.ns1.Local-DNS-Server. (
2020110501
3600
600
259200
86400
)
IN NS ns1.Local-DNS-Server.
IN NS ns2.Local-DNS-Server.
IN PTR Local-DNS-Server.
IN A 255.255.255.0
52 IN PTR yakiniku.Local-DNS-Server.
207 IN PTR ns1.Local-DNS-Server.
217 IN PTR ns2.Local-DNS-Server.
スレーブサーバの設定
# vi /etc/named.conf

//
// named.conf
//
// Provided by Red Hat bind package to configure the ISC BIND named(8) DNS
// server as a caching only nameserver (as a localhost DNS resolver only).
//
// See /usr/share/doc/bind*/sample/ for example named configuration files.
//
// See the BIND Administrator's Reference Manual (ARM) for details about the
// configuration located in /usr/share/doc/bind-{version}/Bv9ARM.html

options {
listen-on port 53 { 127.0.0.1;
192.168.1.217; };
listen-on-v6 port 53 { ::1; };
directory "/var/named";
dump-file "/var/named/data/cache_dump.db";
statistics-file "/var/named/data/named_stats.txt";
memstatistics-file "/var/named/data/named_mem_stats.txt";
recursing-file "/var/named/data/named.recursing";
secroots-file "/var/named/data/named.secroots";
allow-query { any; };

/*
- If you are building an AUTHORITATIVE DNS server, do NOT enable recursion.
- If you are building a RECURSIVE (caching) DNS server, you need to enable
recursion.
- If your recursive DNS server has a public IP address, you MUST enable access
control to limit queries to your legitimate users. Failing to do so will
cause your server to become part of large scale DNS amplification
attacks. Implementing BCP38 within your network would greatly
reduce such attack surface
*/
recursion no;

dnssec-enable yes;
dnssec-validation yes;

/* Path to ISC DLV key */
bindkeys-file "/etc/named.root.key";

managed-keys-directory "/var/named/dynamic";

pid-file "/run/named/named.pid";
session-keyfile "/run/named/session.key";
};

logging {
channel default_debug {
file "data/named.run";
severity dynamic;
};
};

zone "." IN {
type hint;
file "named.ca";
};

include "/etc/named.rfc1912.zones";
include "/etc/named.root.key";

key "master-slave" {                    // 共有鍵の設定
algorithm hmac-md5;
secret "6q5MpifXpE2X5VYPNngXQw==";
};

server 192.168.1.207 {
keys { master-slave; };
};

zone "Local-DNS-Server" IN {
type slave;
masters { 192.168.1.207; };
file "slaves/Local-DNS-Server.db";
};

zone "1.168.192.in-addr.arpa" {
type slave;
masters { 192.168.1.207; };
file "slaves/1.168.192.in-addr.arpa.db";
};
webサーバで確認
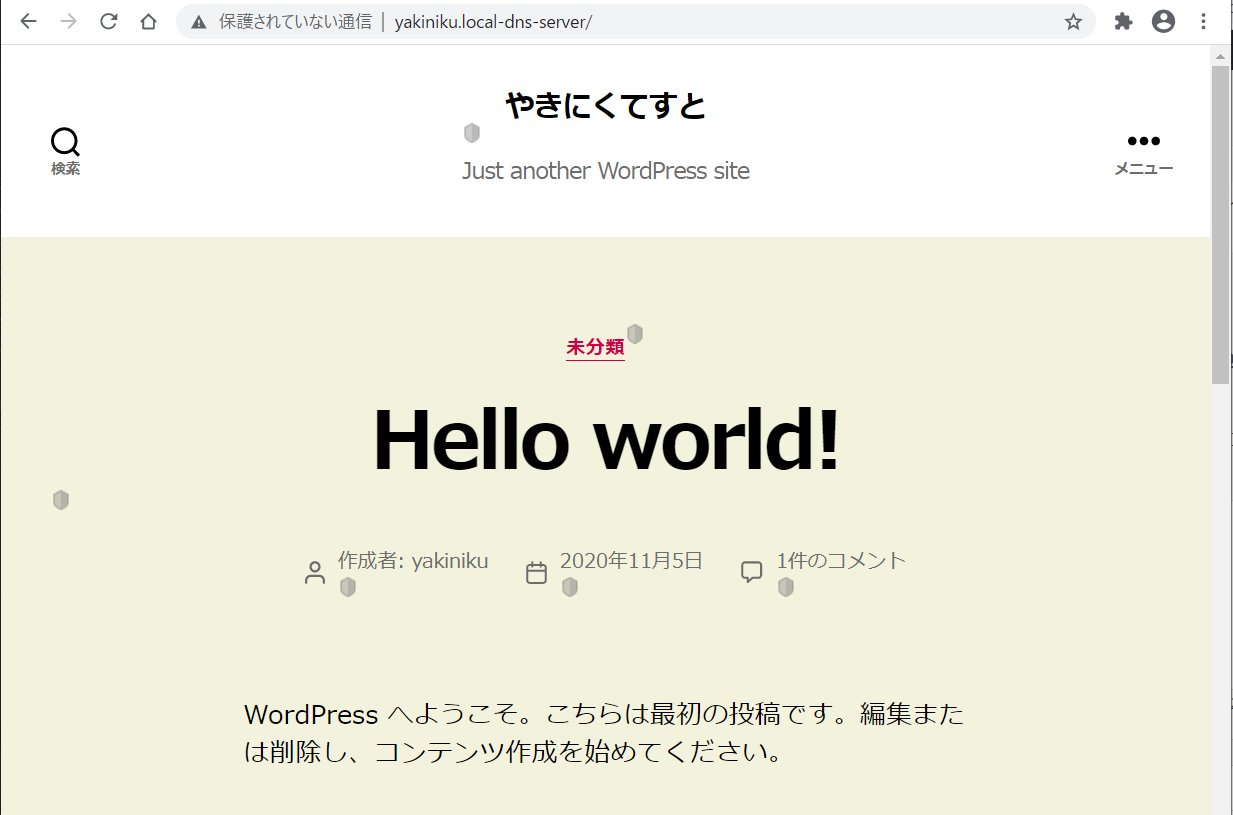
無事ドメインでアクセスできました。
ローカル環境ですと自分が管理者なので、設定変更の自動更新を待たずに手動で反映させられる為、すぐにドメインでアクセスできました。
dig で確認
any で確認
[root@CentOS7-server-test ~]# dig -t any yakiniku.local-dns-server
;; Connection to 127.0.0.1#53(127.0.0.1) for yakiniku.local-dns-server failed: connection refused.

; <<>> DiG 9.11.4-P2-RedHat-9.11.4-16.P2.el7_8.6 <<>> -t any yakiniku.local-dns-server
;; global options: +cmd
;; Got answer:
;; ->>HEADER<<- opcode: QUERY, status: NOERROR, id: 57555
;; flags: qr aa rd; QUERY: 1, ANSWER: 1, AUTHORITY: 2, ADDITIONAL: 3
;; WARNING: recursion requested but not available

;; OPT PSEUDOSECTION:
; EDNS: version: 0, flags:; udp: 4096
;; QUESTION SECTION:
;yakiniku.local-dns-server. IN ANY

;; ANSWER SECTION:
yakiniku.Local-DNS-Server. 86400 IN A 192.168.1.52

;; AUTHORITY SECTION:
Local-DNS-Server. 86400 IN NS ns1.Local-DNS-Server.
Local-DNS-Server. 86400 IN NS ns2.Local-DNS-Server.

;; ADDITIONAL SECTION:
ns1.Local-DNS-Server. 86400 IN A 192.168.1.207
ns2.Local-DNS-Server. 86400 IN A 192.168.1.217

;; Query time: 0 msec
;; SERVER: 192.168.1.217#53(192.168.1.217)
;; WHEN: 木 11月 05 15:13:15 JST 2020
;; MSG SIZE rcvd: 163
逆引きで確認
[root@CentOS7-server-test ~]# dig -x 192.168.1.52

; <<>> DiG 9.11.4-P2-RedHat-9.11.4-16.P2.el7_8.6 <<>> -x 192.168.1.52
;; global options: +cmd
;; Got answer:
;; ->>HEADER<<- opcode: QUERY, status: NOERROR, id: 61099
;; flags: qr aa rd; QUERY: 1, ANSWER: 1, AUTHORITY: 2, ADDITIONAL: 3
;; WARNING: recursion requested but not available

;; OPT PSEUDOSECTION:
; EDNS: version: 0, flags:; udp: 4096
;; QUESTION SECTION:
;52.1.168.192.in-addr.arpa. IN PTR

;; ANSWER SECTION:
52.1.168.192.in-addr.arpa. 86400 IN PTR yakiniku.Local-DNS-Server.

;; AUTHORITY SECTION:
1.168.192.in-addr.arpa. 86400 IN NS ns1.Local-DNS-Server.
1.168.192.in-addr.arpa. 86400 IN NS ns2.Local-DNS-Server.

;; ADDITIONAL SECTION:
ns1.Local-DNS-Server. 86400 IN A 192.168.1.207
ns2.Local-DNS-Server. 86400 IN A 192.168.1.217

;; Query time: 0 msec
;; SERVER: 192.168.1.217#53(192.168.1.217)
;; WHEN: 木 11月 05 15:16:35 JST 2020
;; MSG SIZE rcvd: 161
どちらも WARNING: recursion requested but not available が出ていますが、権威サーバとして再帰問い合わせ無効に設定しているので問題ないです。
まとめ
やってみた感想
困った点
・ named.conf の内容が bind のバージョンによって廃止された設定もあるようで、調整するのに時間がかかりました。
・「 ” 」をひとつ入力漏れがあったのですが、エラーは最終行が74行目なのに75行目で以下の内容でしたので原因を特定するのに、かなり時間がかかりました。
/etc/named.conf:75: unexpected end of input
よかった点
・以前、取得ドメインをクラウドのサーバに割り当てたとき、なかなかうまくいかず設定変更しても 1 回ごとの設定反映まで数時間から数十時間かかっていたので、かなり時間がかかりました。今回は手動で更新したので早かったです。
・今回の検証でドメインの仕組みや設計について勉強になりました。
・名前解決できるとローカル環境でも管理が楽になりそうなので、他のサーバやリモート端末も登録してみようと思います。
コロナ影響でリモートアクセスする機会がかなり増えたので、いつでもどこからでも試したいことが試せる検証環境にしたいと思います。
multicast Domain Name System も気になるので、時間を作って試したいと思います。
お疲れさまでした。